
Recent Posts by Sash:
by Sash, on 22 Dec 2021, 9:13:10 am
2021 has been challenging for the team at Security Centric, as it has for everyone, hopping in and out of lockdowns, an increasing workload and new team members. As we …
Read Storyby Sash, on 16 July 2020, 4:54:49 pm
Background The public figure Twitter account hijacking extends well past social media and has many parallels to business and enterprise systems. Whenever there is a breach, it should be review …
Read Storyby Sash, on 15 Mar 2019, 5:32:45 pm
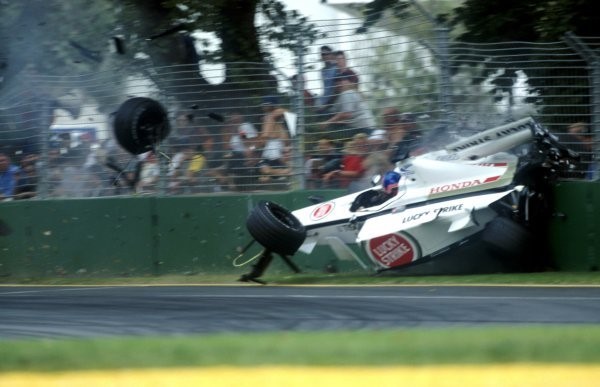
This weekend's Formula 1 Grand Prix has an unlikely parallel to the cyber security industry. You see, Formula 1 is a precisely engineered environment, where suspension load is modelled across …
Read Storyby Sash, on 25 May 2018, 2:58:00 pm
I have been in Europe for a couple of weeks now working on some longer-term strategic initiatives for Security Centric. My work brought me into a larger number of organisations …
Read Storyby Sash, on 17 May 2017, 1:17:00 pm
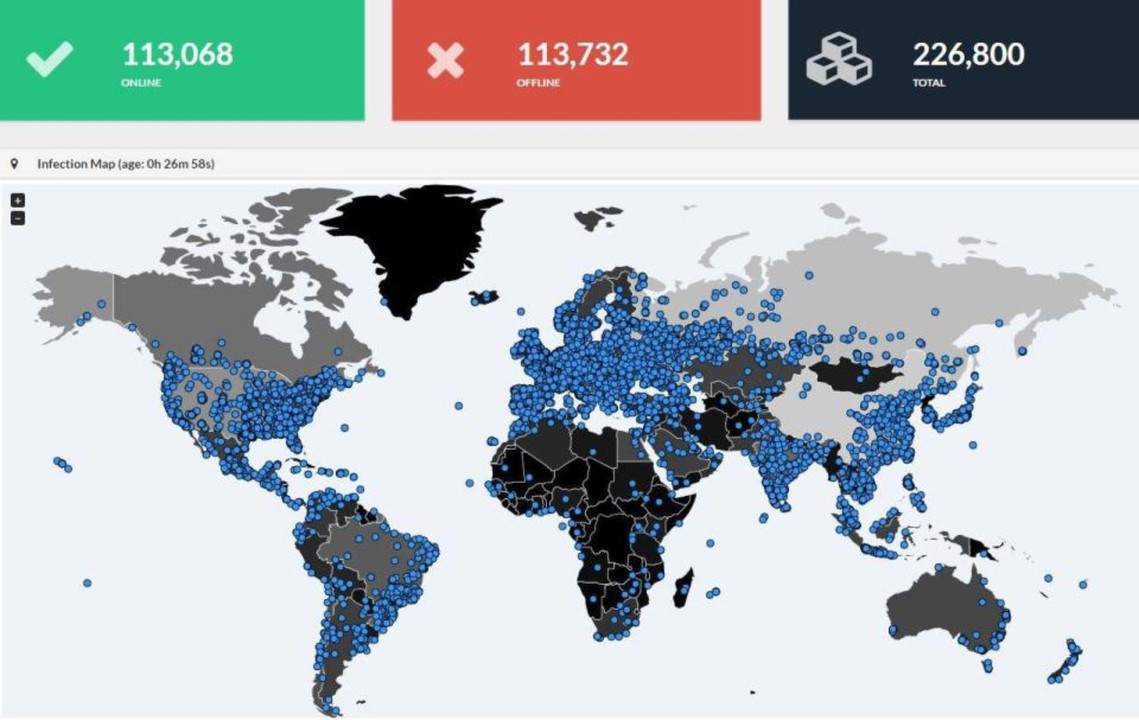
Even the catchy name is not particularly innovative (Heartbleed has to take that prize over others such as BEAST and POODLE). As someone intimately involved in cyber security on a …
Read Storyby Sash, on 14 May 2015, 2:05:00 pm
QSA organisations and individual assessors usually complete the final phase of a PCI DSS compliance program – that is, a final audit. Whilst Security Centric is a QSA organisation, only …
Read Storyby Sash, on 14 Apr 2014, 4:20:00 pm
Much has been written about the OpenSSL Heartbleed vulnerability, which affects the TLS heartbeat mechanism used by some versions of the OpenSSL library. Numerous open source and commercial products use …
Read Story